Microsoft Email Rejections Highlight Why Businesses Need DMARC, SPF and DKIM
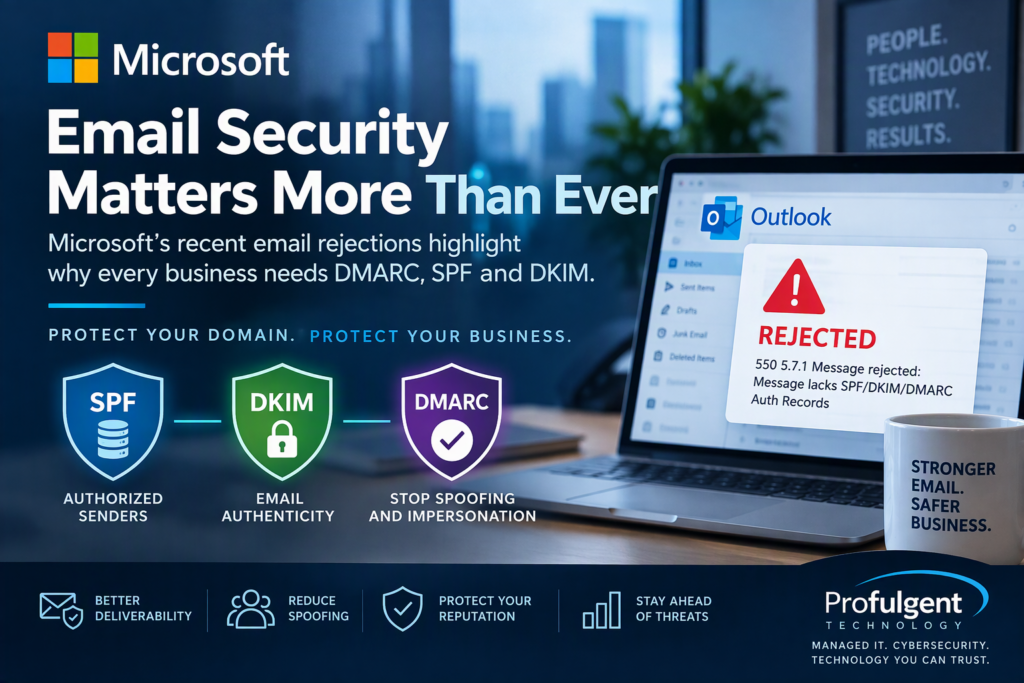
Microsoft Email Rejections Highlight Why Businesses Need DMARC, SPF and DKIM Microsoft DMARC requirements are putting a renewed spotlight on email authentication. Is your business domain properly configured with SPF, DKIM and DMARC? Businesses rely on email every day to communicate with customers, vendors and employees. But a missing or improperly configured DMARC record could affect your email security and, increasingly, your ability to reliably deliver email. In November 2026, businesses began reporting that some email sent to Microsoft Outlook.com, Hotmail.com, Live.com and MSN.com addresses was being rejected when the sending domain did not have a DMARC record. Microsoft later confirmed that the unexpected blocking was caused by an incorrectly deployed spam-enforcement update, which was subsequently rolled back. It was not a new Microsoft policy requiring every email sender to have DMARC. Microsoft Briefly Rejected Mail From Domains Without DMARC. The incident should serve as an important warning to businesses. SPF, DKIM and DMARC are quickly becoming essential components of business email security and reliable email delivery. For businesses using Microsoft 365, Google Workspace, marketing platforms, CRM systems and other cloud services, now is a good time to make sure your domain’s email authentication is properly configured. What Is DMARC? DMARC, or Domain-based Message Authentication, Reporting and Conformance, is an email authentication standard designed to help protect your domain against email spoofing, phishing and other forms of impersonation. DMARC works together with two other important email authentication technologies: SPF (Sender Policy Framework) DKIM (DomainKeys Identified Mail) DMARC is described as an email authentication method that helps prevent spoofed senders commonly used in business email compromise (BEC), phishing and ransomware attacks. Together, SPF, DKIM and DMARC help receiving email providers determine whether a message claiming to come from your company is legitimate. How Do SPF, DKIM and DMARC Work? Business owners don’t need to become email engineers, but understanding what these technologies do is increasingly important. SPF: Who Is Allowed to Send Email? SPF identifies which email systems are authorized to send email on behalf of your domain. For example, your company may authorize Microsoft 365 to send email while also using other services such as a CRM, marketing platform or ticketing system. DKIM: Is the Email Authentic? DKIM applies a digital signature to outgoing email. Receiving email systems use that signature to help verify that the message legitimately came from an authorized system and wasn’t modified in transit. DMARC: Does Everything Match? DMARC ties SPF and DKIM authentication to the domain people actually see in the From address. According to Microsoft, a message passes DMARC when the required SPF or DKIM authentication and domain alignment conditions are satisfied. DMARC can also specify how receiving systems should handle messages that fail authentication. That’s particularly important for protecting your company against criminals pretending to be your employees or executives. Why Did Microsoft Reject Emails Without DMARC? During the November 2026 incident, some senders received errors such as: 550 5.7.1 Message rejected: Message lacks SPF/DKIM/DMARC Auth Records The problem affected some domains even when SPF or DKIM was present. Microsoft subsequently determined that an update to its spam-enforcement rules had incorrectly blocked messages to Microsoft consumer email services. The update was rolled back and Microsoft reported mail flow restored. Microsoft Briefly Rejected Mail From Domains Without DMARC. So why should businesses care if Microsoft fixed the problem? Because email providers are moving toward stronger authentication requirements, particularly for organizations sending large amounts of email. Microsoft already requires domains sending more than 5,000 messages per day to Outlook.com consumer addresses to meet SPF, DKIM and DMARC authentication requirements. Outlook.com Rejected Mail From Domains Without DMARC. The direction of email security is clear. Microsoft 365 or Google Workspace Alone Doesn’t Guarantee Your Domain Is Protected This is one of the biggest misconceptions we see with business email. A company may use Microsoft 365 and assume Microsoft automatically handles everything associated with email authentication. That’s not necessarily the case. Your Microsoft 365 or Google Workspace environment may be configured correctly while another system sends email using your company’s domain. Examples include: CRM systems QuickBooks and accounting applications Marketing platforms Website contact forms Help desk and ticketing systems HR and payroll applications Multifunction printers and scanners Security systems Monitoring platforms Industry-specific business applications Every legitimate service sending email on behalf of your organization needs to be considered when implementing SPF, DKIM and DMARC. Otherwise, improving your security could unintentionally prevent legitimate business applications from sending email. Does My Business Need DMARC? Yes. Even if your organization isn’t currently required by Microsoft to implement DMARC, properly configuring it is a cybersecurity best practice. DMARC can help your organization: Reduce domain spoofing Improve protection against phishing Fight business email compromise Identify unauthorized email senders Improve visibility into who is sending email using your domain Protect your company’s reputation Improve email deliverability Prepare for stricter email authentication requirements DMARC is especially important for companies because email is often one of the most frequently targeted components of a company’s technology environment. What Are DMARC Policies? DMARC allows domain owners to publish instructions telling receiving email providers what to do when messages fail authentication. There are three common policies. DMARC p=none A policy primarily used for monitoring. DMARC p=quarantine A policy primarily used to ask receiving systems to treat authentication failures as suspicious, which may result in those messages being sent to spam or junk folders. DMARC p=reject A policy primarily used to instructs receiving systems to reject messages that fail DMARC authentication. Why DMARC Is a Cybersecurity Issue Protecting email deliverability is only part of the reason businesses should deploy DMARC. The bigger concern is email impersonation. Cybercriminals frequently use email to impersonate: CEOs and executives Accounting personnel Vendors Employees Banks Customers Trusted business partners The attacker may then request a fraudulent wire transfer, change banking information, steal Microsoft 365 credentials or convince an employee to disclose sensitive information. These attacks fall into a broader category commonly called Business Email Compromise (BEC). Microsoft specifically identifies spoofing, BEC, ransomware
AI‑Powered Cyberattacks Are Outpacing Business Defenses | Profulgent
AI‑Powered Cyberattacks Are Outpacing Business Defenses Artificial intelligence has permanently changed the cyber threat landscape. Today’s attackers are leveraging AI to move faster, adapt in real time, and bypass defenses that were considered effective just a few years ago. For small and mid‑sized businesses, this shift has created a dangerous gap between how attacks occur and how security is deployed. AI‑powered cyberattacks are no longer theoretical. They are actively being used to automate phishing, evade endpoint protection, and accelerate ransomware campaigns—often without triggering traditional alerts. Organizations that rely on legacy security tools alone are increasingly exposed. How AI Is Changing the Cyberattack Landscape AI allows attackers to scale and refine their tactics with unprecedented speed. Instead of manually probing defenses, threat actors now use machine learning to identify weaknesses, adjust payloads, and mimic legitimate user behavior. Common examples include: Phishing campaigns that adapt messaging based on user responses Malware that changes its behavior to avoid signature‑based detection Credential attacks that analyze login patterns to evade conditional access controls These attacks are faster, quieter, and far more difficult to detect using conventional tools. Why Traditional Security Tools Can’t Keep Up Firewalls, antivirus software, and periodic scans were designed for a slower threat environment. AI‑driven attacks exploit that limitation by operating between monitoring intervals and disguising malicious activity as normal behavior. Key gaps include: Alert fatigue caused by excessive false positives Lack of behavioral analysis across users and devices Limited visibility into lateral movement after initial compromise Without continuous monitoring and correlation across systems, modern attacks frequently go unnoticed until damage has already occurred. The Real‑World Impact on Small & Mid‑Sized Businesses While large enterprises often dominate cybersecurity headlines, small and mid‑sized organizations are frequently targeted because their defenses are easier to bypass. The most common outcomes include: Business disruption caused by ransomware or system lockouts Data exposure involving client, financial, or regulated information Emergency recovery costs that exceed planned IT budgets In many cases, organizations discover weaknesses only after an incident forces an unplanned response. What Modern Cyber Defense Requires Today Defending against AI‑powered threats requires a shift from reactive security to continuous, intelligence‑driven protection. Effective modern defense strategies typically include: Continuous monitoring through managed detection and response (MDR) Behavioral analytics that identify abnormal activity early Documented incident response plans tested before an event occurs Security controls aligned to real business risk—not just compliance checklists The goal is early detection, rapid containment, and minimal business impact. How Profulgent Helps Reduce AI‑Driven Cyber Risk Profulgent works with organizations to modernize their security posture without overwhelming internal teams. Our approach focuses on visibility, preparedness, and alignment between technology and business objectives. We help clients: Identify security gaps before attackers do Implement monitoring designed for evolving threats Improve response readiness through practical, tested playbooks The result is a security program that evolves as fast as today’s threat landscape—without unnecessary complexity. Concerned About AI‑Driven Cyber Threats? If you’re unsure whether your current defenses can withstand modern attacks, we can help you assess risk and prioritize the right next steps. Schedule a Security Alignment Discussion
Anthropic’s New AI Is a Wake‑Up Call—But Small Business Cybersecurity Habits Are Missing the Real Lesson
Artificial intelligence is advancing fast, and lately the headlines have taken a darker turn. For small business cybersecurity habits, this shift matters more than many owners realize. Some AI tools are now capable of identifying software vulnerabilities and helping security teams—or attackers—move faster than ever before. A recent article from Wired discusses Anthropic’s new AI model, Claude Mythos, and how it’s being framed as a potential “cybersecurity reckoning.” According to Wired, the model is powerful enough to analyze code, uncover weaknesses, and help chain together exploits at a scale humans never could—but its arrival doesn’t mean hackers suddenly gained magic powers. Instead, it exposes a problem that’s been there all along: insecure systems and slow response habits. [technewstube.com] And that’s the part small businesses should be paying attention to. The Real Risk Isn’t New AI—It’s Old Assumptions Many small businesses hear stories like this and think: Unfortunately, that thinking is exactly what puts smaller organizations at risk. What tools like Mythos reveal is that attackers don’t need custom tactics for every business anymore. They exploit common weaknesses: Those conditions are far more common in small businesses than large enterprises. Why This Matters More for Small Businesses Than Big Ones Large companies expect breaches. They have: Small businesses usually don’t. When vulnerabilities are discovered faster—whether by people or AI—the window to fix them shrinks. Businesses that patch monthly, rely on manual updates, or “get to it when they can” are the ones most exposed. AI didn’t create this problem.It just made it visible. What Business Owners Should Focus On: Small Business Cybersecurity Habits This isn’t about AI replacing hackers—it’s about forcing organizations to confront decades of security shortcuts. [technewstube.com] From a small‑business perspective, the biggest takeaways are practical: You don’t need cutting‑edge AI defenses—but you do need consistency. Practical Steps That Actually Reduce Risk Without getting technical, here’s what matters most right now: These steps stop the vast majority of real‑world attacks—AI or not. The Bottom Line AI headlines can make cybersecurity feel abstract or overwhelming. But the lesson from Anthropic’s Mythos—and Wired’s coverage—is actually simple: The businesses that struggle aren’t the ones without powerful tools.They’re the ones relying on outdated habits. Small businesses don’t need to panic.They need to be intentional. And that’s exactly where thoughtful IT guidance makes the difference. You don’t need more tools—you need better habits.A focused IT review can show where small changes reduce real risk. Most small businesses don’t fail at cybersecurity because of sophisticated attacks—they fail because small issues linger too long. Outdated systems, unclear ownership, and delayed fixes quietly increase risk over time. A short, focused IT review can identify where old habits are creating unnecessary exposure—and show which practical changes will have the biggest impact first. That kind of clarity helps business owners move forward with confidence instead of reacting after something breaks.